Cybersecurity Blog

Cybersecurity Research from the Front Lines

Threat research, infrastructure analysis, and operational guidance from the Team Cymru intelligence team, drawn from the global network visibility we maintain across the internet.

Who
Team Cymru's own threat analysts and researchers, writing from the investigations they run.
What
Named threat actors, mapped command-and-control infrastructure, ransomware toolkit teardowns, and the pivot methodology behind them. 150+ posts and counting.
How
Sourced from Team Cymru's own internet-scale network telemetry. We analyze what we see directly, not third-party feeds or aggregated reporting.
When
New analysis every week, plus rapid posts when a campaign breaks.
Why
So defenders get operational detail they can act on inside a SOC or intel workflow. Published in full, with no gate and no registration wall.
Filter
Sorted Newest first
Jeremy Bender

Team Cymru Supports Europol to Takedown of Three Key Cybercriminal Tools as Part of Operation Endgame

Incident Response & Preemptive Defense
November 14, 2025
Team Cymru provided critical data to Europol, leading to the massive disruption of over 1,000 malicious servers and the arrest of a major cybercriminal. See the full Operation Endgame report.
Kyle Contorno

No Scans. No Noise. Just Complete Exposure Visibility

Incident Response & Preemptive Defense
November 12, 2025
The infrastructure you don't know about will hurt you. RADAR delivers complete, passive asset discovery using real network traffic. Stop active scanning risks.

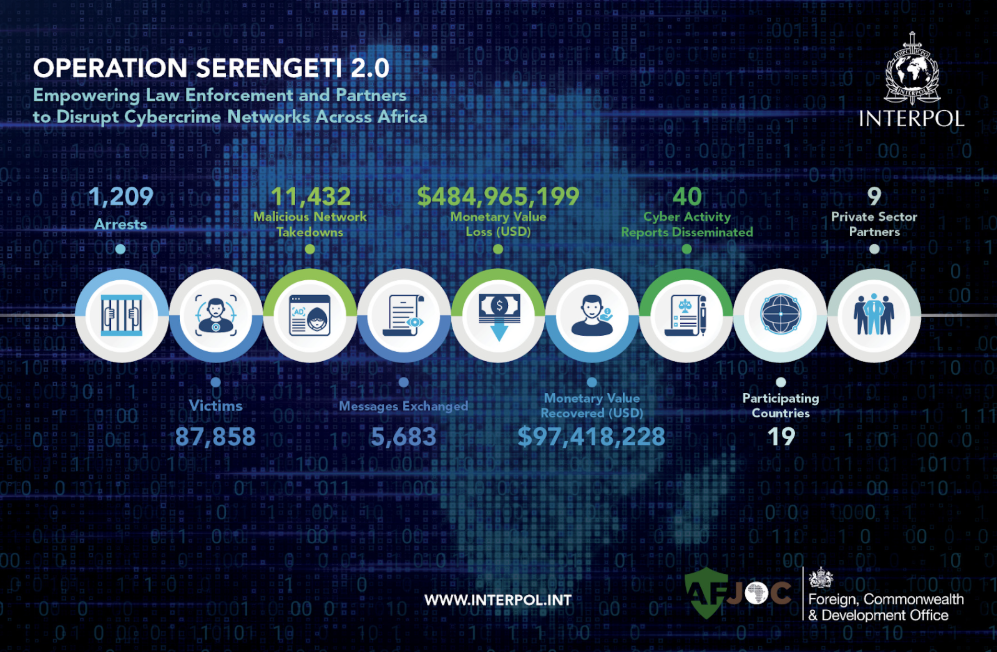
Team Cymru Supports INTERPOL’s Operation Serengeti 2.0 to Dismantle Cybercrime Networks Across Africa

Incident Response & Preemptive Defense
August 26, 2025
Team Cymru supported INTERPOL's Operation Serengeti 2.0, which led to 1,209 arrests and dismantled 11,432 malicious infrastructures across Africa.
Lewis Henderson

Supercharge Threat Hunting: Team Cymru Pure Signal™ Scout Now Integrated with Google SecOps

SOC Enablement & Intelligence Enrichment
August 11, 2025
Team Cymru's Pure Signal Scout now integrates with Google SecOps, adding internet-scale NetFlow context to investigations, threat hunting, and response.
Will Thomas

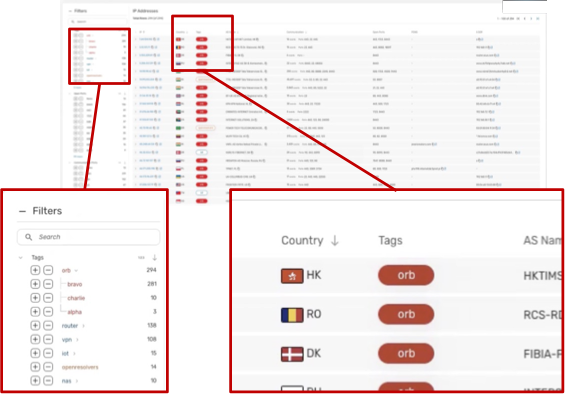
Fingerprinting Malware C2s with Tags

Malware & Ransomware Analysis
August 4, 2025
This blog is written for threat analysts, defenders, and CTI teams who use our Scout platform—but even if you’re not a user today, it offers practical insight into how advanced research teams fingerprint C2 infrastructure, and how you might apply similar methods using your tools.
tcblogposts

Team Cymru Tags Explained: Powering Faster, Smarter Threat Intelligence

Cloud & Application Security
August 1, 2025
Discover how Team Cymru Tags deliver real-time context to analysts, enabling faster triage, better threat detection, and automation-ready intelligence. Learn more.
Eli Woodward

ToolShell, SharePoint, and the Death of the Patch Window

Cloud & Application Security
July 8, 2025
This blog explores this week's zero-day exploit targeting Microsoft SharePoint, now referred to as ToolShell, caught organizations off guard.
Will Thomas

Supply Chain & CTI

Cloud & Application Security
July 8, 2025
This blog explores how cyber threat intelligence (CTI) must change and support a new approach to supply chain risk.
Will Thomas

Uncovering DPRK Remote Workers: Detecting Hidden Threats Through Internet Telemetry

Malware & Ransomware Analysis
June 30, 2025
This blog explores unpacks key insights and explains how internet telemetry can be used to detect these threats in the real world.
S2 Research Team

Inside DanaBot’s Infrastructure: In Support of Operation Endgame II

Incident Response & Preemptive Defense
May 22, 2025
This blog explores DanaBot a "malware-as-a-service" and how collaboration across the security community can lead to real progress against threat actors
tcblogposts

Understanding the Federal Compliance Landscape

Malware & Ransomware Analysis
March 12, 2025
Explore how federal agencies can align compliance mandates like NIST SP 800-171, CMMC, and FISMA with proactive threat intelligence for stronger security.
Andrew Korty

Team Cymru Achieves ISO 27001 Re-Certification for Third Consecutive Year

Incident Response & Preemptive Defense
March 11, 2025
Team Cymru earns ISO 27001 re-certification for the third year, reinforcing its commitment to security, compliance, and protecting customer data. Learn more.

Stay in the loop

Stay current with Team Cymru insights

Get the latest research, articles, and threat intelligence resources, delivered straight to your inbox.