

Feed Threat Signals
Threat feed integrations deliver real-time malicious infrastructure signals to keep you ahead of attackers.
Law enforcement brings the authority. Team Cymru brings the visibility to map the infrastructure worth disrupting: 35K+ servers taken down, 2,300+ arrests supported, 95+ nations in coordination.
One workspace that brings Scout, Recon and Radar together, so analysts can investigate, enrich and act in one place.
Team Cymru sees traffic between networks a defender does not own. NetFlow turns that vantage point into evidence of what happened, in what order, and where it went next.
See inside supplier and partner networks, spot compromise, and act before it reaches your organization.
RISE brings regional security leaders together for focused, high-signal sessions. Underground Economy is the invite-only global conference on cybercrime ecosystems and adversary economics.
Autonomous hacking tools still depend on servers and scanning infrastructure. Learn how to spot offensive AI before it reaches your network, with Eli Woodward, Senior Threat Intelligence Advisor at Team Cymru.
Curated cyber threat news, research, incidents and events direct to your inbox. A daily email digest, at no cost.
NetFlow Advantage Use Case
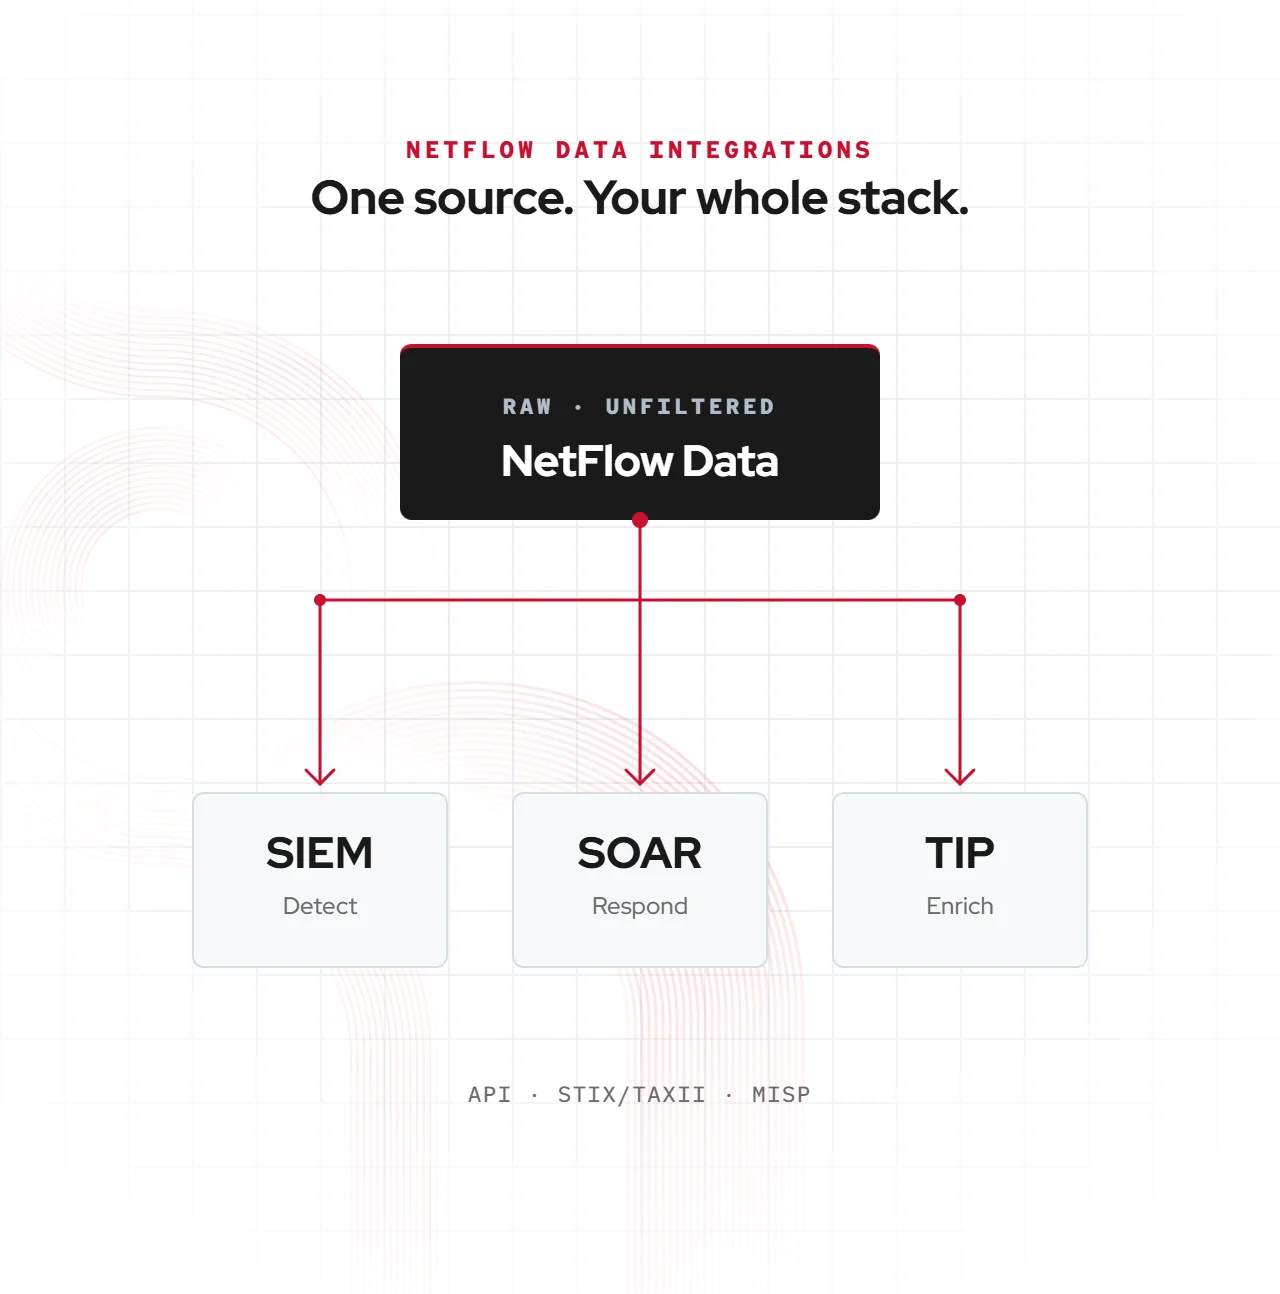
Fuel existing defenses with raw NetFlow streams for automated blocking and enrichment
Why it matters
Most commercial threat intelligence feeds rely on “finished” intelligence that is outdated, incomplete, and littered with vendor interpretation/bias. This limits the effectiveness of your SIEM, SOAR, and TIP systems, leaving risky blind spots, dulling the power of your security stack, and reducing ROI.
Unlock the power of your SIEM, SOAR, and TIP systems by powering them with raw telemetry from 1,000+ validated global NetFlow sources.
How it works
Threat feed integrations deliver real-time malicious infrastructure signals to keep you ahead of attackers.

Automatically activate blocking or remediation workflows that eliminate manual interventions.

Add behavioral context to individual alerts, helping analysts quickly identify the highest-risk events.

Link alerts and events across systems based on live actor activity to reveal broader attack patterns.
What it reveals

See threat activity as it happens, instead of relying on delayed, partial, or pre-processed feeds.

Get a complete view of attacker behavior, not just IOCs, so your team can proactively disrupt threats.
Map command-and-control, reconnaissance, staging, and callback activity across attacker infrastructure.
Signals

Trigger automated blocks on malicious IPs and infrastructure to stop threats before they reach your network.

Add context to alerts with C2 activity details, giving analysts faster access to actionable intelligence.

Link alerts from multiple systems by mapping shared infrastructure to uncover broader attack patterns.

Threat feed integrations spot reconnaissance activity before attackers gain a foothold in your environment.

Enhance threat intelligence platform scoring with real-time behavioral and infrastructure attributes.

Validate malicious activity before triggering automated remediation workflows.
Comparison
| Capability | Team Cymru | Commercial Threat Feeds | CTI Platforms |
|---|---|---|---|
| Real-time visibility | Yes | No | Partial |
| Behavioral indicators | Yes | No | Partial |
| Infrastructure mapping | Yes | No | Partial |
| Pre-compromise detection | Yes | No | No |
| Historical + live coverage | Yes | No | Partial |
Who uses it

Enrich alerts, reduce false positives, and accelerate response time.
Automate high-confidence blocking actions to stop threats faster.
Correlate infrastructure across campaigns and tools to map threat landscapes.
Related use cases
 01/04
Know immediately when threat actors start surveilling, probing, and mapping your infrastructure for attack access points.
Explore Use Cases 02/04
Gain visibility into your extended vendor ecosystem, identifying risky connections, exposed services, and potential attack vectors.
Explore Use Cases 03/04
Visualize attacker infrastructure and malware campaigns to see how threats are connected across the internet.
Explore Use Cases 04/04
Reconstruct the full attack chain from first recon to current activities, using decades of flow data.
Explore Use CasesSee why Team Cymru is the leader in real-time data integrations that enhance your SIEM, SOAR, and TIP systems with global NetFlow visibility.