Cybersecurity Blog

Cybersecurity Research from the Front Lines

Threat research, infrastructure analysis, and operational guidance from the Team Cymru intelligence team, drawn from the global network visibility we maintain across the internet.

Who
Team Cymru's own threat analysts and researchers, writing from the investigations they run.
What
Named threat actors, mapped command-and-control infrastructure, ransomware toolkit teardowns, and the pivot methodology behind them. 150+ posts and counting.
How
Sourced from Team Cymru's own internet-scale network telemetry. We analyze what we see directly, not third-party feeds or aggregated reporting.
When
New analysis every week, plus rapid posts when a campaign breaks.
Why
So defenders get operational detail they can act on inside a SOC or intel workflow. Published in full, with no gate and no registration wall.
Filter
Sorted Newest first
Wassim Tawbi

New innovation helps Security Teams gain faster threat insights

API, Platform & Hybrid Visibility Risk
March 5, 2025
Team Cymru's Insights Feed helps security teams cut through noise, reduce false positives, and gain real-time, actionable threat intelligence for faster response.
David Monnier

Top 10 Predictions Shaping the Future of Cybersecurity in 2025 According to 35+ Experts

Attack Surface & Exposure Visibility
February 22, 2025
Explore the top 10 cybersecurity predictions for 2025, based on insights from industry leaders shaping the future of threat intelligence and security strategy.
David Monnier

Splunk's Security Strategist on Building Effective Threat Hunting Programs

Threat Hunting & Detection Engineering
February 15, 2025
Splunk’s David Bianco shares threat hunting tips, team-building strategies, and how to use red teaming to improve detection capabilities and security operations.
David Monnier

Google's Head of Security Architecture Shares Framework for Protecting AI Systems

Real-Time Threat Detection & Signals
February 11, 2025
Google’s Head of Security Architecture shares a real-world framework for protecting AI systems from evolving threats like model poisoning and prompt injection.
S2 Research Team

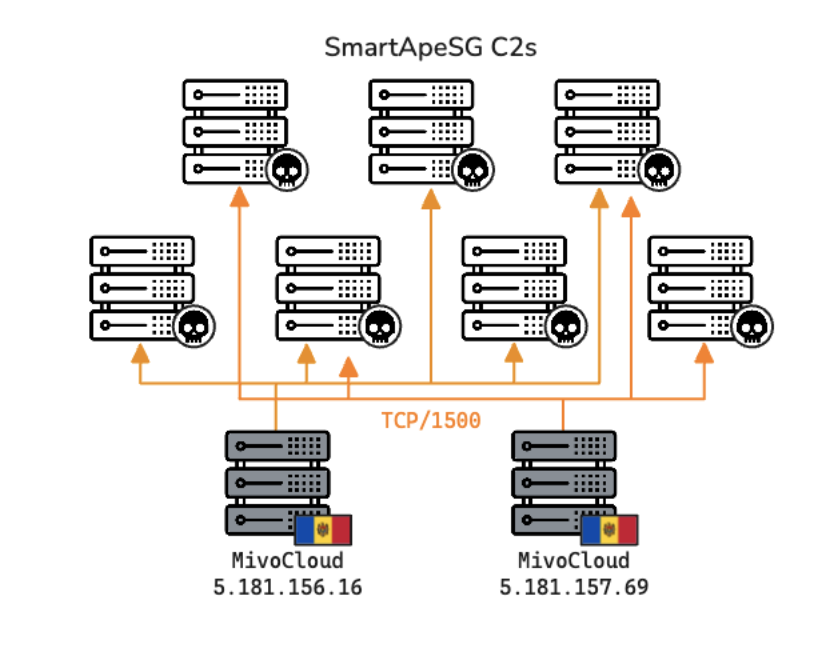
Tracing the Path From SmartApeSG to NetSupport RAT

NetFlow & Traffic Intelligence
February 3, 2025
Investigation reveals how SmartApeSG delivers NetSupport RAT, exposing links to RAT clusters, crypto services, and suspicious infrastructure. Learn more.
David Monnier

Building a More Resilient Security Strategy Through Threat Intelligence Integration

Executive Strategy, Risk & ROI
January 24, 2025
Strengthen your security strategy by integrating threat intelligence to improve response, reduce risk, and build proactive defenses amid rising cyber threats.
Lewis Henderson

Eating Your Own Dog Food

Real-Time Threat Detection & Signals
January 2, 2025
Explore how Team Cymru's SecOps team uses its own threat intel tools—Scout, Recon, and more—for faster investigations, proactive hunting, and automation.
Lewis Henderson

DORA Regulation (Digital Operational Resilience Act): A Threat Intelligence Perspective

Threat Hunting & Detection Engineering
January 2, 2025
Discover DORA compliance from a threat intel lens—understand penalties, visibility gaps, and how to strengthen operational resilience before the 2025 deadline.
Lewis Henderson

A Primer on JA4+: Empowering Threat Analysts with Better Traffic Analysis

Incident Response & Preemptive Defense
December 23, 2024
JA4+ enhances threat analysis by providing precise insights into encrypted traffic, helping analysts detect malware and anomalies faster and more accurately.
S2 Research Team

Jingle Shells: How Virtual Offices Enable a Facade of Legitimacy

Threat Reports & Intelligence Briefings
December 20, 2024
Virtual offices provide flexibility but also enable fraudsters to establish shell companies. Learn how this trend impacts businesses and regulations globally.
Kyle Contorno

2024 Year in Review: Features and Improvements in Pure Signal™ Scout

Threat Hunting & Detection Engineering
December 13, 2024
Team Cymru is excited to share our accomplishments in delivering new features and improvements in Pure Signal™ Scout.
David Monnier

Team Cymru Honored with Third Consecutive Gold HIRE Vets Medallion Award from U.S. Department of Labor

Threat Reports & Intelligence Briefings
November 11, 2024
Team Cymru earns third consecutive Gold HIRE Vets Medallion Award, recognizing commitment to hiring, supporting, and developing veterans in meaningful careers.

Stay in the loop

Stay current with Team Cymru insights

Get the latest research, articles, and threat intelligence resources, delivered straight to your inbox.