

Rebuild Attacker Activity
Recon to initial access sequences
Law enforcement brings the authority. Team Cymru brings the visibility to map the infrastructure worth disrupting: 35K+ servers taken down, 2,300+ arrests supported, 95+ nations in coordination.
One workspace that brings Scout, Recon and Radar together, so analysts can investigate, enrich and act in one place.
Team Cymru sees traffic between networks a defender does not own. NetFlow turns that vantage point into evidence of what happened, in what order, and where it went next.
See inside supplier and partner networks, spot compromise, and act before it reaches your organization.
RISE brings regional security leaders together for focused, high-signal sessions. Underground Economy is the invite-only global conference on cybercrime ecosystems and adversary economics.
Autonomous hacking tools still depend on servers and scanning infrastructure. Learn how to spot offensive AI before it reaches your network, with Eli Woodward, Senior Threat Intelligence Advisor at Team Cymru.
Curated cyber threat news, research, incidents and events direct to your inbox. A daily email digest, at no cost.
NetFlow Advantage Use Case
Trace an attack chain from inception to current activity with decades of historical NetFlow data analysis.
Why it matters
Critical breach evidence disappears fast, making data-driven root cause analysis a complex challenge for DFIR teams.
Only NetFlow preserves all original network activity. But most organizations rely on just a handful of NetFlow streams. Complete incident reconstruction requires maximum global NetFlow visibility, which only Team Cymru provides.
How it works
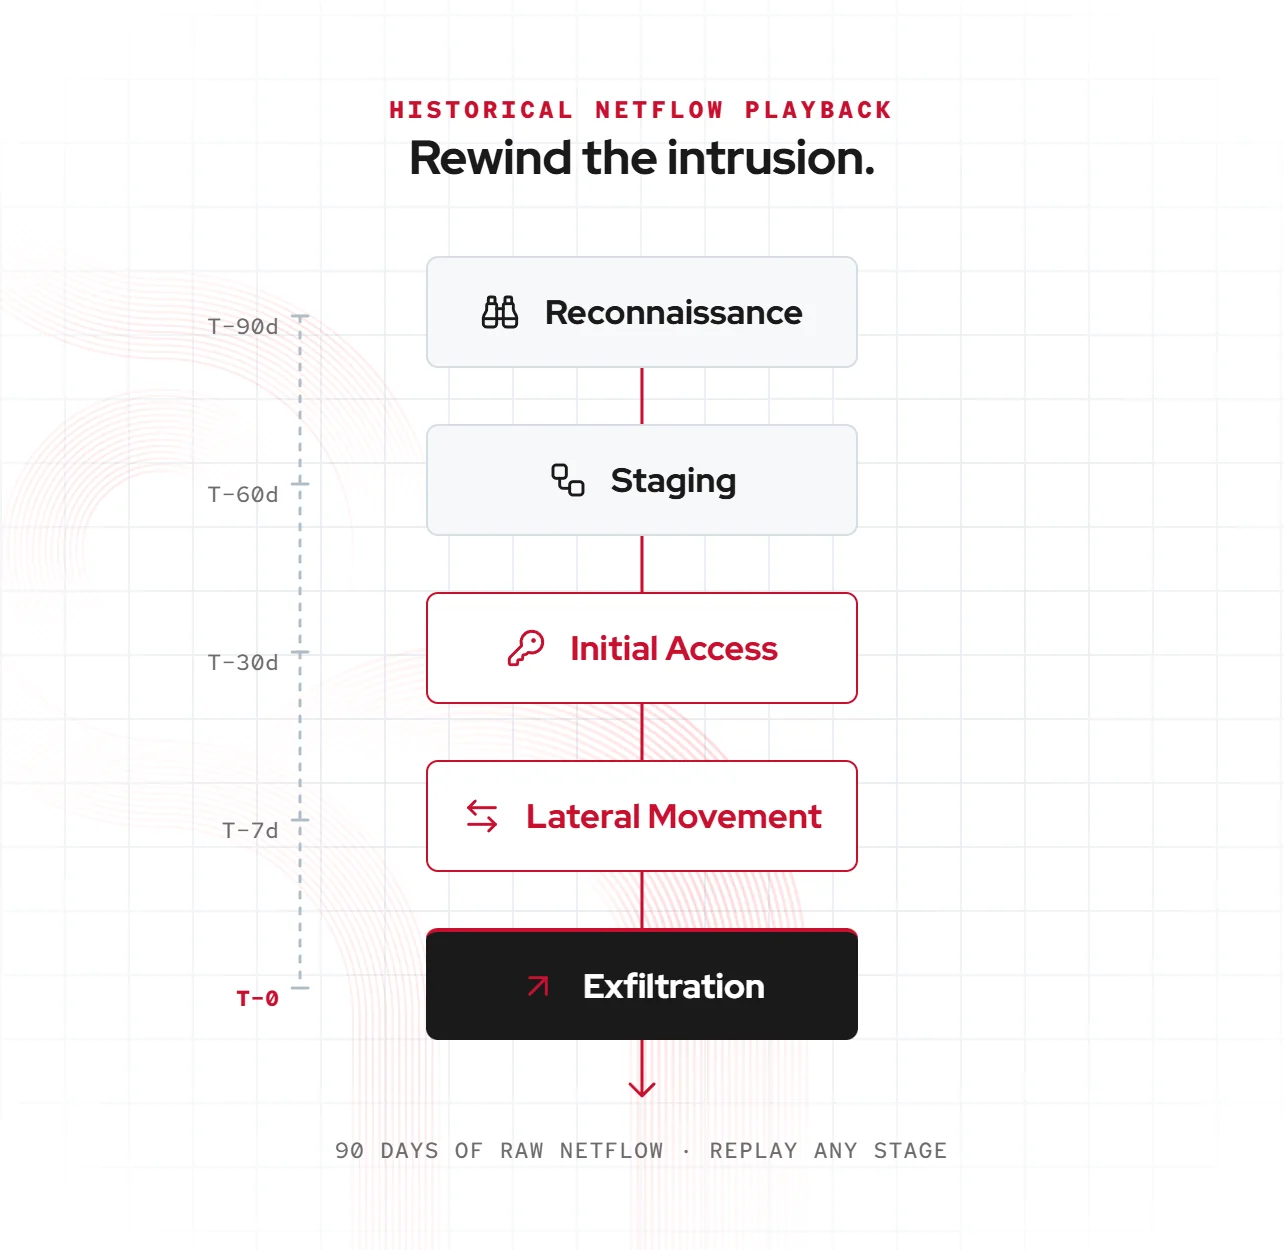
Track intrusions across every phase with 1,000+ global NetFlow sources powering every step of your forensic network analysis
Recon to initial access sequences

Beaconing and command paths

Staging to compromise progression

Data movement and exit paths
What it reveals

See months to years of NetFlow for full campaign context

Track fallback nodes, C2 rotations, and operator changes

Uncover prior recon and failed exploit attempts
Signals

Reveal infrastructure staged during threat reconnaissance, in advance of active use.

Surface the earliest attempts to gain access to blind spots in your environment.

Know exactly when compromised hosts first reached out to malicious infrastructure.

Track movements between cloud, hybrid, on‑prem systems, and your entire supply chain.

Connect incidents to broader malware and botnet operations.

Compare past activity patterns against what’s unfolding now, in real time.
Comparison
| Capability | Team Cymru | SIEM | EDR | Cloud Logs |
|---|---|---|---|---|
| Long-term historical visibility | Yes,20+ Years | Partial | No | No |
| Reconstruct full external attack chain | Yes | No | No | No |
| Detect pre-compromise recon | Yes | No | No | No |
| Map infrastructure evolution | Yes | No | No | No |
| Fill gaps from deleted/tampered logs | Yes | No | No | No |
Who uses it

Validate attack timelines while conducting a data-driven root cause analysis.
Spot missed detections and track actor infrastructure patterns.
Trace campaign lineage and understand infrastructure evolution.
Related use cases
 01/04
Know immediately when threat actors start surveilling, probing, and mapping your infrastructure for attack access points.
Explore Use Cases 02/04
Gain visibility into your extended vendor ecosystem, identifying risky connections, exposed services, and potential attack vectors.
Explore Use Cases 03/04
Visualize attacker infrastructure and malware campaigns to see how threats are connected across the internet.
Explore Use Cases 04/04
Stream real-time NetFlow data directly into existing security stack to accelerate detection, investigation, and response.
Explore Use CasesDefend your organization with historical and real-time threat visibility.