

Real-Time Supplier Monitoring
See which suppliers are talking to known threat actor infrastructure within minutes.
Law enforcement brings the authority. Team Cymru brings the visibility to map the infrastructure worth disrupting: 35K+ servers taken down, 2,300+ arrests supported, 95+ nations in coordination.
One workspace that brings Scout, Recon and Radar together, so analysts can investigate, enrich and act in one place.
Team Cymru sees traffic between networks a defender does not own. NetFlow turns that vantage point into evidence of what happened, in what order, and where it went next.
See inside supplier and partner networks, spot compromise, and act before it reaches your organization.
RISE brings regional security leaders together for focused, high-signal sessions. Underground Economy is the invite-only global conference on cybercrime ecosystems and adversary economics.
Autonomous hacking tools still depend on servers and scanning infrastructure. Learn how to spot offensive AI before it reaches your network, with Eli Woodward, Senior Threat Intelligence Advisor at Team Cymru.
Curated cyber threat news, research, incidents and events direct to your inbox. A daily email digest, at no cost.
NetFlow Advantage Use Case
See active malicious connections within supplier and partner networks in real time.
Why it matters
Supply chain security threats sit outside traditional visibility, highlighting an urgent problem: you can’t defend what you can’t see. With 90% of organizations citing third-party compromise as their top risk, external attack surface monitoring is mission critical.
Leveraging the most comprehensive collection of global NetFlow sources, Team Cymru delivers behavioral evidence of compromise across external networks, giving you maximum visibility before attackers can infiltrate your infrastructure.
We own the only real-time and global view into external supply chain compromise.
How it works
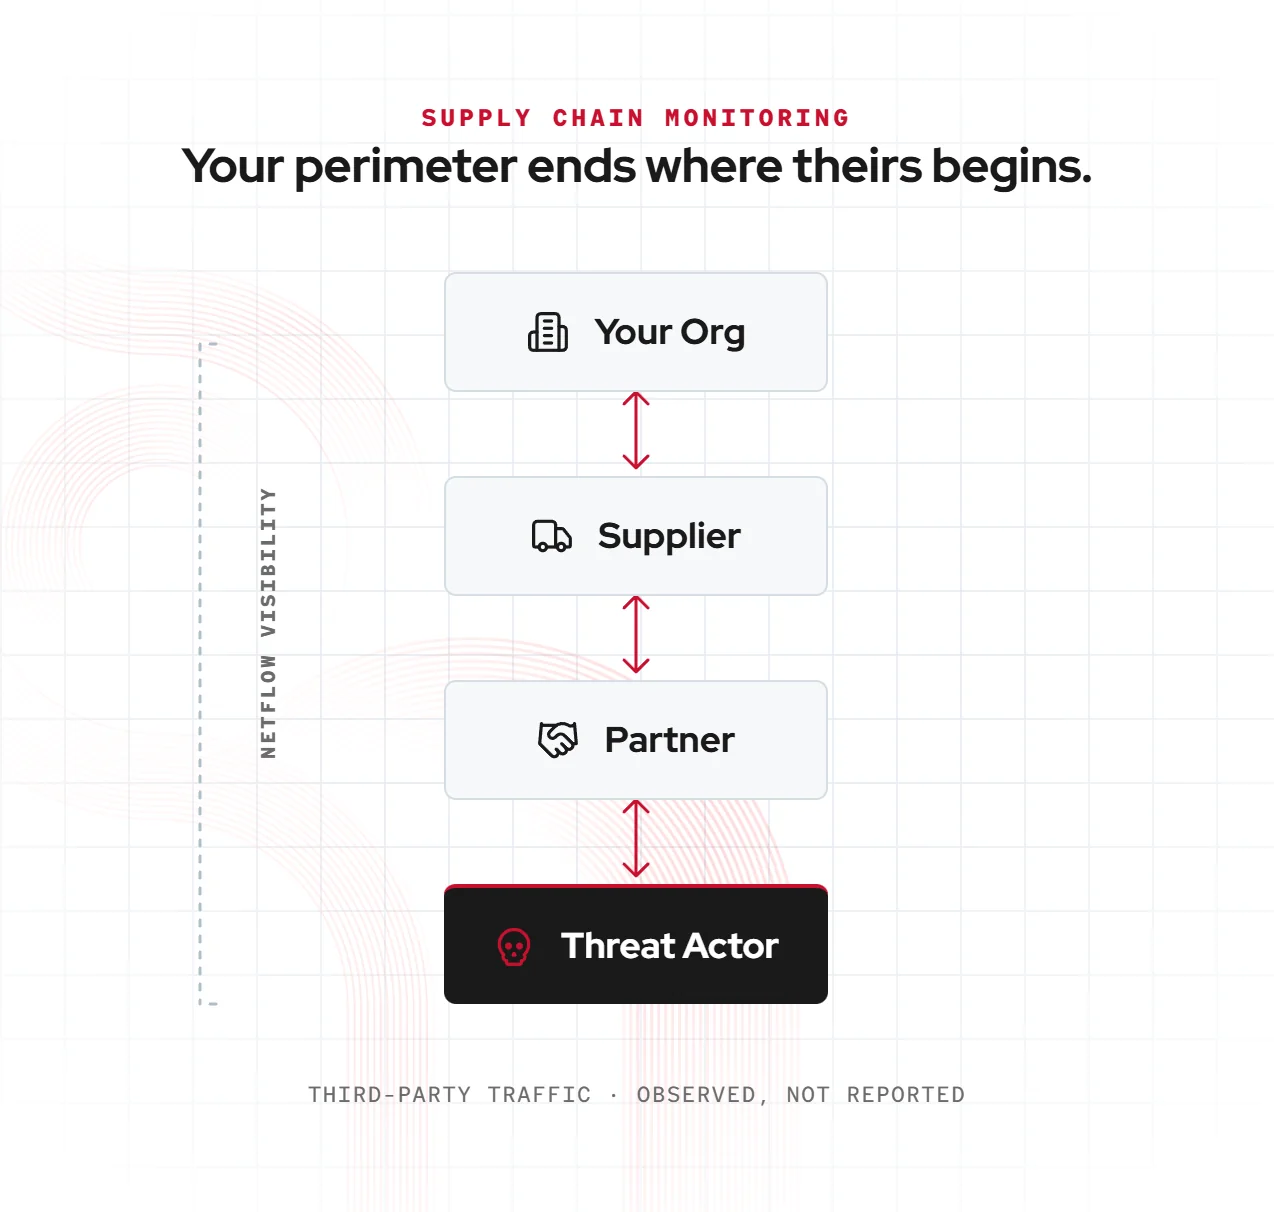
With the world’s most extensive collection of raw NetFlow data sources, Team Cymru exposes the supply chain cyber security threats that go unseen by traditional cybersecurity tools.
See which suppliers are talking to known threat actor infrastructure within minutes.

Spot scanning, staging, and C2 callback activity across global networks in real time.

Trace lateral infections and links between compromised vendors and attacker systems.
What it reveals

Detect C2 callbacks, scanning, and data exfiltration paths in real time.
Track threat actor infrastructure from supplier IPs to broader campaign activity.

Reveal cross-partner or vendor infections spreading laterally across networks.
Signals
Tactical clarity on supply chain cyber security threats for analysts and CISOs alike
Spot suppliers talking to known command-and-control infrastructure in real time.

Detect repeated traffic from suppliers to risky or suspicious IP ranges.

Identify probing and scanning activity originating from vendor networks.

Reveal when attacker staging systems come online in partner environments.
Track unusual lateral activity spreading across vendor ecosystems.

Monitor abrupt spikes in network flows that may indicate compromise.
Comparison
See the difference in our supply chain security threat detection capabilities.
| Capability | Team Cymru | DRP/ASM | CTI | SIEM |
|---|---|---|---|---|
| Detects active malicious traffic in vendor networks | Yes | No | No | No |
| Real-time behavioral indicators | Yes | No | Partial | No |
| Infrastructure mapping across partners | Yes | No | No | No |
| Historical campaign context | Yes | No | Partial | No |
Who uses it

Prioritize third-party risk in real time. Identify compromised suppliers before they become attack vectors. Validate vendor security posture with live behavioral evidence rather than static questionnaires.
Confirm supply chain security threats and map attacker infrastructure across vendor networks. Correlate real-time raw flows with historical behavior to uncover hidden attacker activity.
Build preemptive defenses to block malicious vendor communications. Detect reconnaissance, staging, and lateral movement using raw source insights instead of filtered threat assessments with inherited vendor bias.
Related use cases
Explore ways to leverage our NetFlow for real-time external attack surface monitoring
 01/04
Know immediately when threat actors start surveilling, probing, and mapping your infrastructure for attack access points.
Explore Use Cases 02/04
Visualize attacker infrastructure and malware campaigns to see how threats are connected across the internet.
Explore Use Cases 03/04
Replay and analyze past and current network flows to uncover hidden threats and early-stage compromise.
Explore Use Cases 04/04
Stream real-time NetFlow data directly into existing security stack to accelerate detection, investigation, and response.
Explore Use CasesGain live visibility into partner and supply chain security threats with our unmatched NetFlow vendor risk monitoring