

Detect Scanning & Mapping Patterns
Identify systematic probing and repeated hits on specific ports, hosts, and network segments as attackers map your environment.
Law enforcement brings the authority. Team Cymru brings the visibility to map the infrastructure worth disrupting: 35K+ servers taken down, 2,300+ arrests supported, 95+ nations in coordination.
One workspace that brings Scout, Recon and Radar together, so analysts can investigate, enrich and act in one place.
Team Cymru sees traffic between networks a defender does not own. NetFlow turns that vantage point into evidence of what happened, in what order, and where it went next.
See inside supplier and partner networks, spot compromise, and act before it reaches your organization.
RISE brings regional security leaders together for focused, high-signal sessions. Underground Economy is the invite-only global conference on cybercrime ecosystems and adversary economics.
Autonomous hacking tools still depend on servers and scanning infrastructure. Learn how to spot offensive AI before it reaches your network, with Eli Woodward, Senior Threat Intelligence Advisor at Team Cymru.
Curated cyber threat news, research, incidents and events direct to your inbox. A daily email digest, at no cost.
NetFlow Advantage Use Case
Detect probing and staging activity against critical infrastructure before compromise.
Why it matters
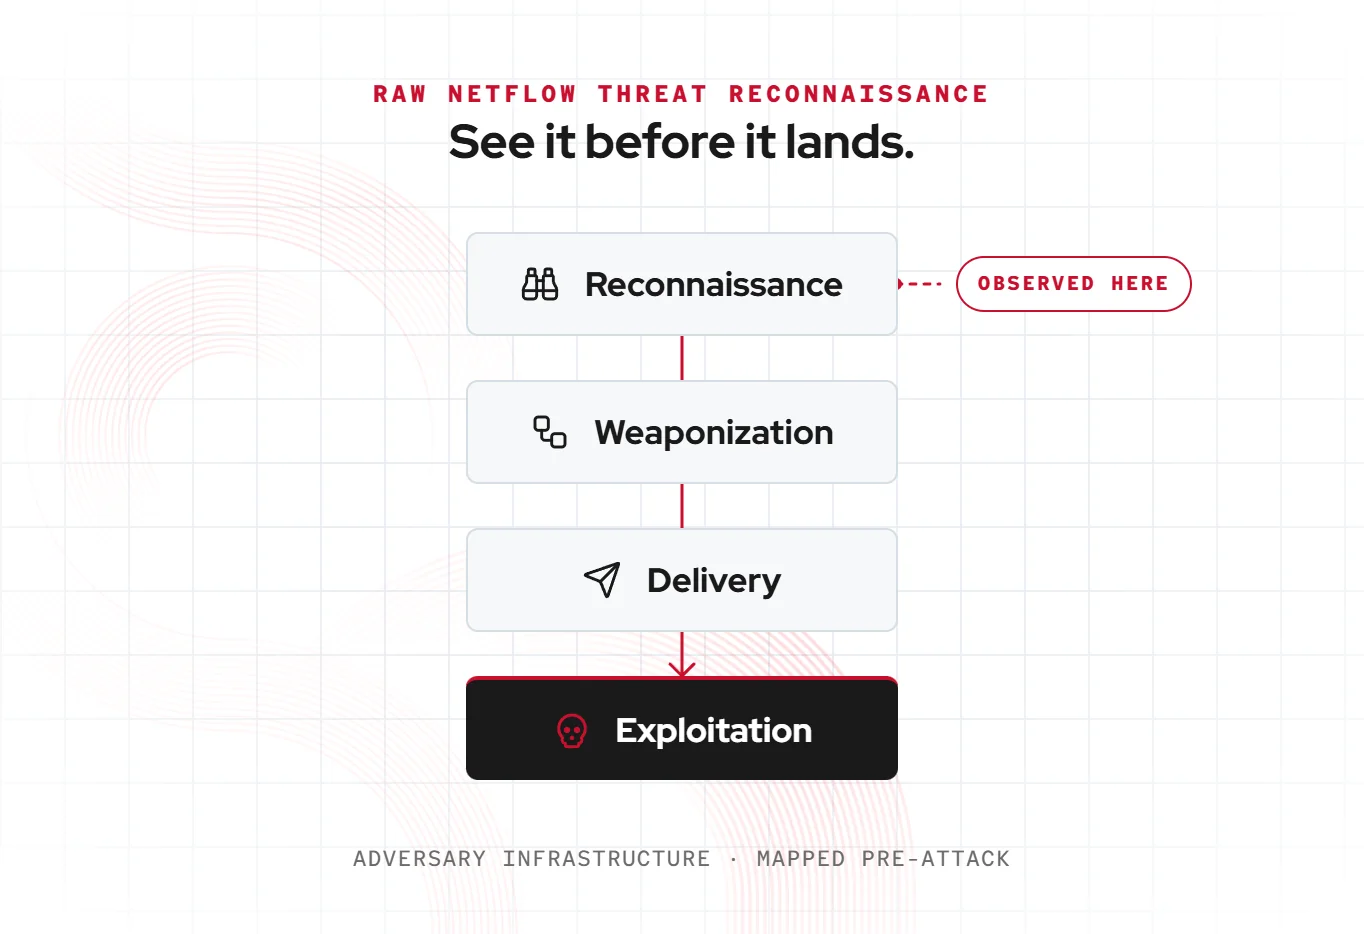
Cyberattacks always start with network reconnaissance. Threat actors probe, scan, and map your infrastructure, looking for blind spots to penetrate. But instead of alerting you during this reconnaissance stage, traditional security tools don’t ping until attacks are already underway, far too late.
NetFlow data exposes threat reconnaissance in real time, giving you the visibility to detect and disrupt attacks before damage occurs.
How it works
Identify systematic probing and repeated hits on specific ports, hosts, and network segments as attackers map your environment.

Spot slow, distributed reconnaissance patterns engineered to blend in and evade detection from SIEM and EDR tools.

See staging infrastructure the minute it comes online, often the earliest sign an attacker is preparing for initial access.

Reveal beaconing, callback tests, and abnormal paths between known C2 infrastructure and unknown external IPs.
What it reveals

See recon attempts across the worldwide Internet, not just inside your perimeter.

Get live visibility into network reconnaissance as it’s happening, not after the fact.

Amplify investigative context by tracing any recon event over months or years.
Signals

Expose large-scale scanning operations targeting specific industries or technologies.

Reveal attackers preparing lateral movement through unusual connections between internal hosts.

Spot the early stages of credential-harvesting operations as they prepare to gather log-in credentials.

Identify reconnaissance probes aimed at critical systems and sensitive data stores.

Show how threat actors map cloud services and resources to locate potential attack paths.

Track beaconing and callback activity from endpoints to inactive command-and-control infrastructure.
Comparison
| Capability | Team Cymru | SIEM | TIP | CTI | DRP |
|---|---|---|---|---|---|
| Detects actor recon early | Yes | No | No | No | No |
| Real-time infrastructure mapping | Yes | No | No | No | No |
| Sees global activity | Yes | No | No | No | Partial |
| Exposure to novel adversary infrastructure | Yes | No | Partial | No | No |
Who uses it

Identify and block malicious infrastructure before exploits launch.
Prioritize alerts based on verified pre-compromise reconnaissance signals.
Attribute operators and track campaigns during early development.
Related use cases
External Threat Reconnaissance is one part of a broader visibility advantage only available with Team Cymru. Explore how the same raw NetFlow vantage point powers additional high-impact use cases.
 01/04
Locate malicious connections within supplier and partner networks in real time.
Explore Use Cases 02/04
Reconstruct the full attack chain from first recon to current activities, using decades of flow data.
Explore Use Cases 03/04
Attribute callbacks to operator infrastructure and track malware ecosystems over time.
Explore Use Cases 04/04
Automate blocking and enrichment with raw NetFlow monitoring for cyber threat defense.
Explore Use CasesDiscover how our comprehensive collection of raw NetFlow data reveals network reconnaissance long before attackers invade your perimeter.