

Trace Infected Hosts to Operator Nodes
Follow flow-level activity from compromised endpoints to the operator infrastructure behind them, revealing command execution, beaconing rhythms, and early pivot behavior.
Law enforcement brings the authority. Team Cymru brings the visibility to map the infrastructure worth disrupting: 35K+ servers taken down, 2,300+ arrests supported, 95+ nations in coordination.
One workspace that brings Scout, Recon and Radar together, so analysts can investigate, enrich and act in one place.
Team Cymru sees traffic between networks a defender does not own. NetFlow turns that vantage point into evidence of what happened, in what order, and where it went next.
See inside supplier and partner networks, spot compromise, and act before it reaches your organization.
RISE brings regional security leaders together for focused, high-signal sessions. Underground Economy is the invite-only global conference on cybercrime ecosystems and adversary economics.
Autonomous hacking tools still depend on servers and scanning infrastructure. Learn how to spot offensive AI before it reaches your network, with Eli Woodward, Senior Threat Intelligence Advisor at Team Cymru.
Curated cyber threat news, research, incidents and events direct to your inbox. A daily email digest, at no cost.
NetFlow Advantage Use Case
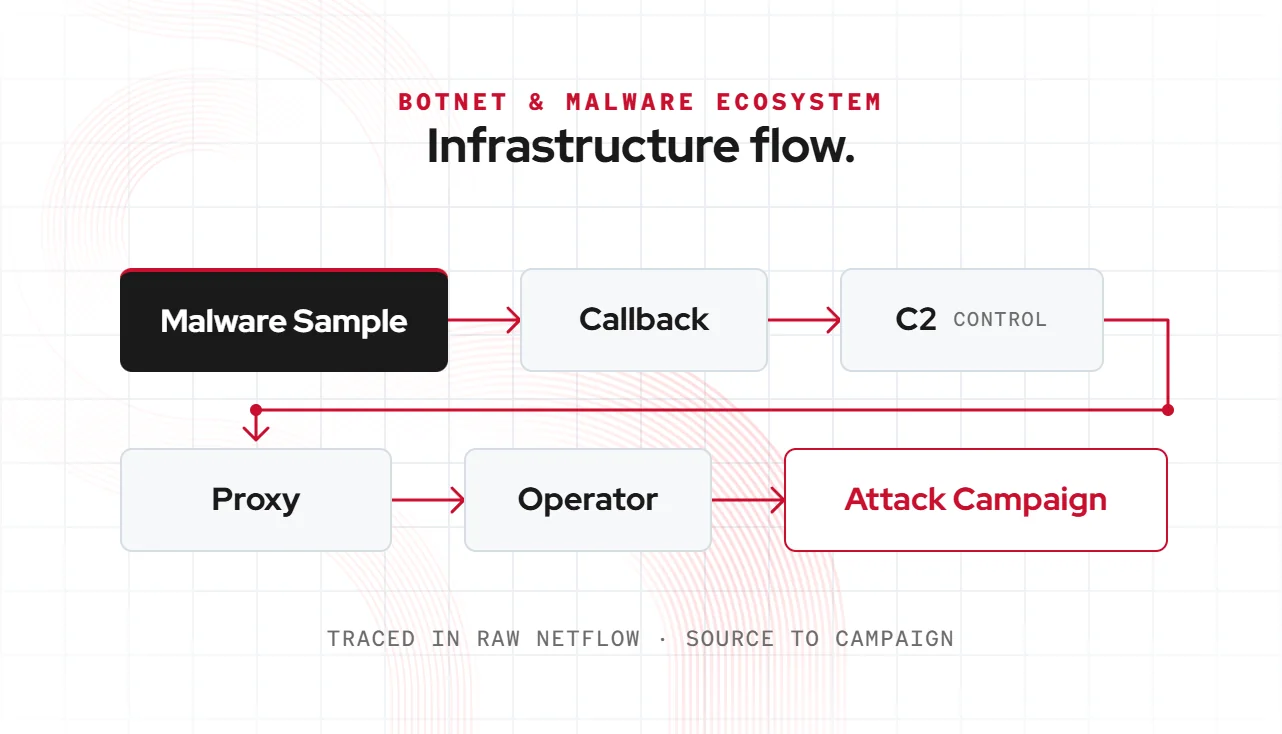
Attribute malware callbacks using raw flow data to link them to operator infrastructure.
Why it matters
Malware threat intelligence no longer relies on a single file. Instead, it requires visibility into a distributed ecosystem. Threat actors operate across staging servers, proxy nodes, bulletproof hosting, and multiple C2 families.
Team Cymru delivers real-time, global NetFlow visibility across the entire malware and botnet ecosystem. See into external networks so you can detect, map, and disrupt attacks before they reach your environment.
How it works
Uncover the structural visibility that NetFlow provides for botnet malware analysis across ecosystems.
Follow flow-level activity from compromised endpoints to the operator infrastructure behind them, revealing command execution, beaconing rhythms, and early pivot behavior.
Surface the relationships between C2 servers, proxy chains, and staging infrastructure, uncovering the backbone nodes that support multiple malware families.
Observe how botnet components span regions and providers, mapping cross‑geography infrastructure patterns that traditional threat feeds never reveal.
What it reveals
Analyze timing, frequency, and “phone-home” paths from infected hosts to understand attacker communication behavior.
Reveal multi-node command-and-control setups, including proxies, redirectors, and fallback hosts supporting malware operations.
Map connections between malware families and shared operators to uncover broader campaign-level infrastructure relationships.
Signals
Get tactical malware threat intelligence insights, with continuous visibility as threat actor behavior evolves.

Spot newly activated command-and-control nodes as they come online in real time.

Observe sudden surges in beaconing and communication from infected hosts.

Track malware families extending operations into new regions and networks.

Identify backup servers and alternate pathways used when primary infrastructure fails.

Reveal attempts by malware to move laterally across internal or partner networks.

Expose shared nodes and resources used across multiple malware families and campaigns.
Comparison
See what makes our botnet malware analysis capabilities different.
| Capability | Team Cymru | CTI Feeds | Sandboxes | EDR/Endpoint |
|---|---|---|---|---|
| Real-time observation of C2 callbacks | Yes | No | Partial | Partial |
| See entire malware ecosystem | Yes | No | No | No |
| Detect infrastructure reuse across campaigns | Yes | No | No | No |
| Attribute operators via behavior | Yes | No | Partial | No |
Who uses it

Leverage global NetFlow to understand attacker infrastructure, relationships, and emerging malware campaigns.

Use raw telemetry to identify and prevent malware and botnets from infiltrating your network.

Investigate incidents with complete internal and external visibility into attacker behavior and network compromise.
Related use cases
 01/04
Know immediately when threat actors start surveilling, probing, and mapping your infrastructure for attack access points.
Explore Use Cases 02/04
Gain visibility into your extended vendor ecosystem, identifying risky connections, exposed services, and potential attack vectors.
Explore Use Cases 03/04
Replay and analyze past and current network flows to uncover hidden threats and early-stage compromise.
Explore Use Cases 04/04
Stream real-time NetFlow data directly into existing security stack to accelerate detection, investigation, and response.
Explore Use CasesSee the full picture of malware and botnets activity to stay ahead of emerging threats.