October 14, 2026
LegionRelay: Ukraine Targeted by Five Previously Unidentified C2 Servers
In recent months, two separate but complementary pieces of research have shed light on a cluster of malicious infrastructure targeting Ukraine. WithSecure published its GREYVIBE report, and Ukraine's national CERT (CERT-UA) issued its own advisory tracking the same threat actor activity.
During March and April 2026, CERT-UA recorded an intensification of cyberattacks against local Ukrainian government bodies and, primarily, municipal healthcare institutions. The attacks were carried out via email under the guise of discussing a proposal for providing humanitarian aid, during which the attacker encouraged the recipient to click on a link. CERT-UA noted that the targets of these campaigns may also include representatives of the Defense Forces of Ukraine.
WithSecure researchers noted that this threat has been active since at least August 2025 and observed that the adversary’s actions on objectives align with the interests of the Russian state, particularly in support of intelligence gathering. While the activities appear to be state-sponsored, the researchers also observed some signs that ties the adversary to current or former cybercriminal actors.
This blog walks through how a CTI Analyst or Threat Hunter can take the indicators published in these two reports and use Team Cymru to pivot across the shared infrastructure characteristics, surfacing additional, previously unreported command-and-control (C2) servers belonging to the same activity cluster.
GREYVIBE LegionRelay C2 servers
The GREYVIBE report describes a family of C2 servers associated with a malware referred to as LegionRelay. It is a PowerShell-based RAT that was likely developed with large language model (LLM) assistance and uses REST API methods to communicate.
Across the servers WithSecure documented, a consistent set of infrastructure attributes emerged:
- Hosted on AS26383
- Listening on Port 8000
- Presenting a "France Education" open-port banner
- Running a Uvicorn ASGI server
The IP addresses WithSecure shared for this cluster were:
- 89.125.189.118:8000
- 89.125.189.85:8000
- 91.149.221.124:8000
- 194.87.128.243:8000
- 194.87.108.110:8000
UAC-0247 C2 Servers
CERT-UA tracks the corresponding activity under the designation UAC-0247. The C2 servers it published overlap with and extend the GREYVIBE set, and notably sit on the same ASN (AS26383).
The IP addresses CERT-UA shared for this cluster were:
- 89.125.189.118:8000
- 91.149.221.9:8000
- 91.149.253.100:8000
- 194.87.108.110:8000
Interestingly, these IP addresses “194.87.108.110” and “89.125.189.118” appeared in both the GREYVIBE and CERT-UA reports.
Pivoting in Team Cymru Scout
Rather than treating the published indicators as a static list, we used their shared characteristics as a fingerprint. The combination of the ASN, port 8000, and the distinctive "France Education" banner were specific enough to isolate this cluster, while broad enough to catch servers that neither report observed.
In Team Cymru Scout, that fingerprint translated into a single Scout query:
openports.banner = "France Education" asn = "26383" openports.port = "8000"
Pivoting on this fingerprint returned the known reported servers and, crucially, surfaced additional hosts sharing the exact same configuration that were not named in either the GREYVIBE or CERT-UA reporting.
The IP addresses uncovered by Team Cymru for this cluster were:
- 91.149.221.118:8000
- 91.149.221.123:8000
- 166.88.239.54:8000
- 194.87.108.12:8000
- 194.87.108.217:8000
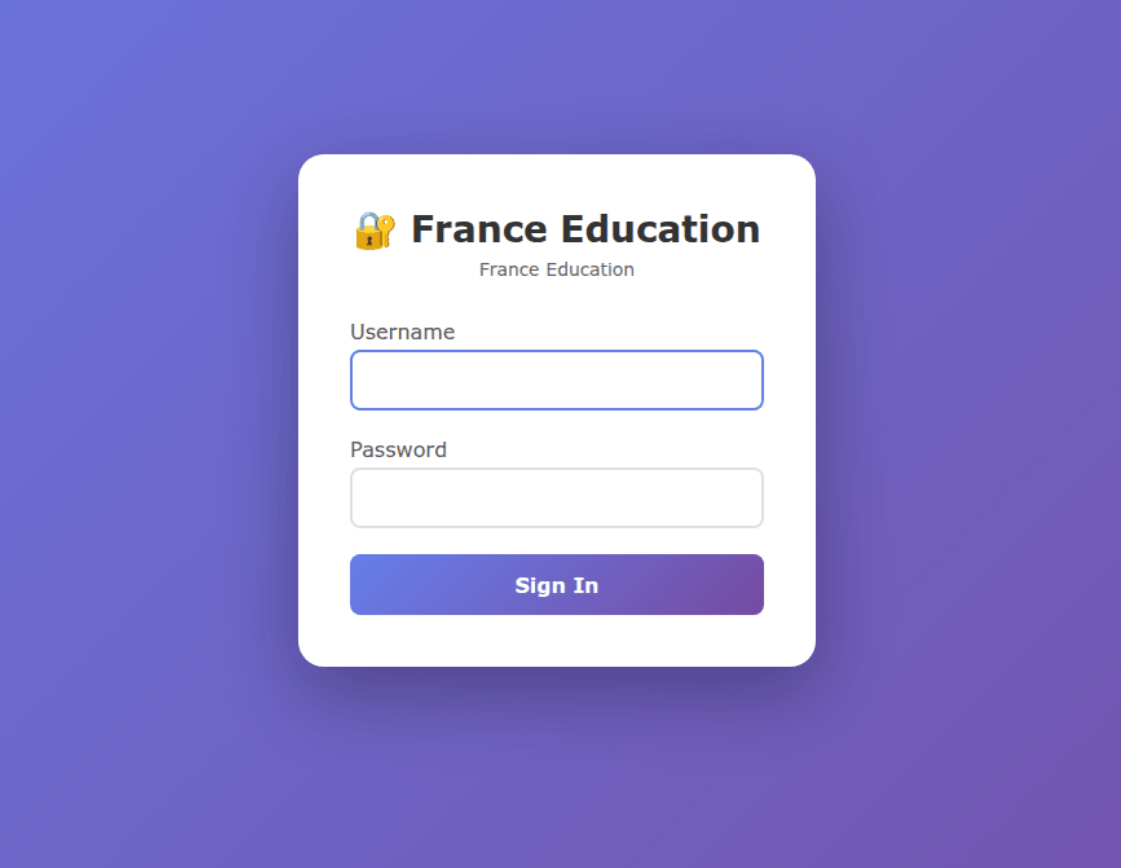
Analysis of the content on these IP addresses, when they were active, revealed the live LegionRelay C2 Login Page. Notably, this was identical to the Login Page that greeted the WithSecure researchers during their analysis.
Conclusion
By combining the indicators from two independent reports and abstracting them into a behavioural and infrastructural fingerprint, we were able to move beyond a static indicator list to proactively map the wider footprint of this Russia-aligned cluster.
The consistent use of port 8000, and the reused port banner made this infrastructure pivotable in Team Cymru Scout. The pivot yielded five additional C2 candidates not present in the original reporting.
Defenders monitoring for Russia-aligned threats should consider blocking or alerting on the indicators below, and Team Cymru customers may wish to run the same Scout pivot periodically to catch newly provisioned servers as the operators rotate their infrastructure.