Threat Intelligence Solutions
Command: Advanced Threat Intelligence
AI Threat Intelligence AccessPassive Asset Discovery ToolProactive Threat Hunting ToolsReal-Time Threat Intelligence
Global Network VisibilityActionable Threat Intelligence Feeds
Use Cases
Netflow Advantage
Botnet & MalwareSupply ChainRoot Cause AnalysisRaw DataDirect Data Feeds
Fraud Defense IntelligenceSupply Chain and Risk ThreatsRansomwareNation-State Threat ActorsPhishingFinancial Sector
Global Defender Exchange
Operational Marketplace
Bogon NetworksDDOS Mitigation UTRSNimbus Threat MonitorMHR - APICSIRT Assistance ProgramIP-to-ASN Mapping
News Bytes SubscriptionRISEUnderground Economy
Customers
Resources
BlogPodcast - Future of Threat IntelligencePodcast - Dragon News BytesEventsWebinarsResources LibraryIntelligence TermsIntegrations
Partners
Resellers, MSPs & SIs
Technology Alliance Partners
GoogleMicrosoftPalo AltoSplunkTinesThreatQuotientCywareVertexOpenCTI
API IntegrationBecome a Partner
Company
About UsNewsPress ReleasesCareersContact Us
Talk To an expert
tcblogposts
0
min read

May 22, 2024

Want to learn more about NetFlow? Here's a useful analogy to get you started

Infographic explaining NetFlow using a train analogy, with a train passing a router station, introducing NetFlow as a tool for monitoring malicious activity and improving internet security
NetFlow train analogy: internet data packets are like boxcars on trains traveling between cities, and routers are the depots that direct them along the tracks to their destination
NetFlow sampling explained: like depot workers counting one boxcar per train, routers sample about 1 in 3,000 to 1 in 10,000 packets and record source IP, destination IP, ports, and packet counts, but not content
How NetFlow data supports threat intelligence: spotting boxcars of a certain size and color reveals the source and destination of illicit shipments, much like tracking traffic to command and control (C2) servers
NetFlow conveys no content: it confirms communication between two endpoints, helping defenders reveal malicious infrastructure behind DDoS, ransomware, and credential theft

‍

Copy Link

The latest articles straight to your inbox

Related Posts

Scott Fisher
5
min read

Relaying to the Frontier

From the disk to the flows: ransomware infrastructure analysis of Akira, DragonForce, Clop, and other ransomware gangs
Will Thomas
4
min read

From the Disk to the Flows: Ransomware Infrastructure Analysis

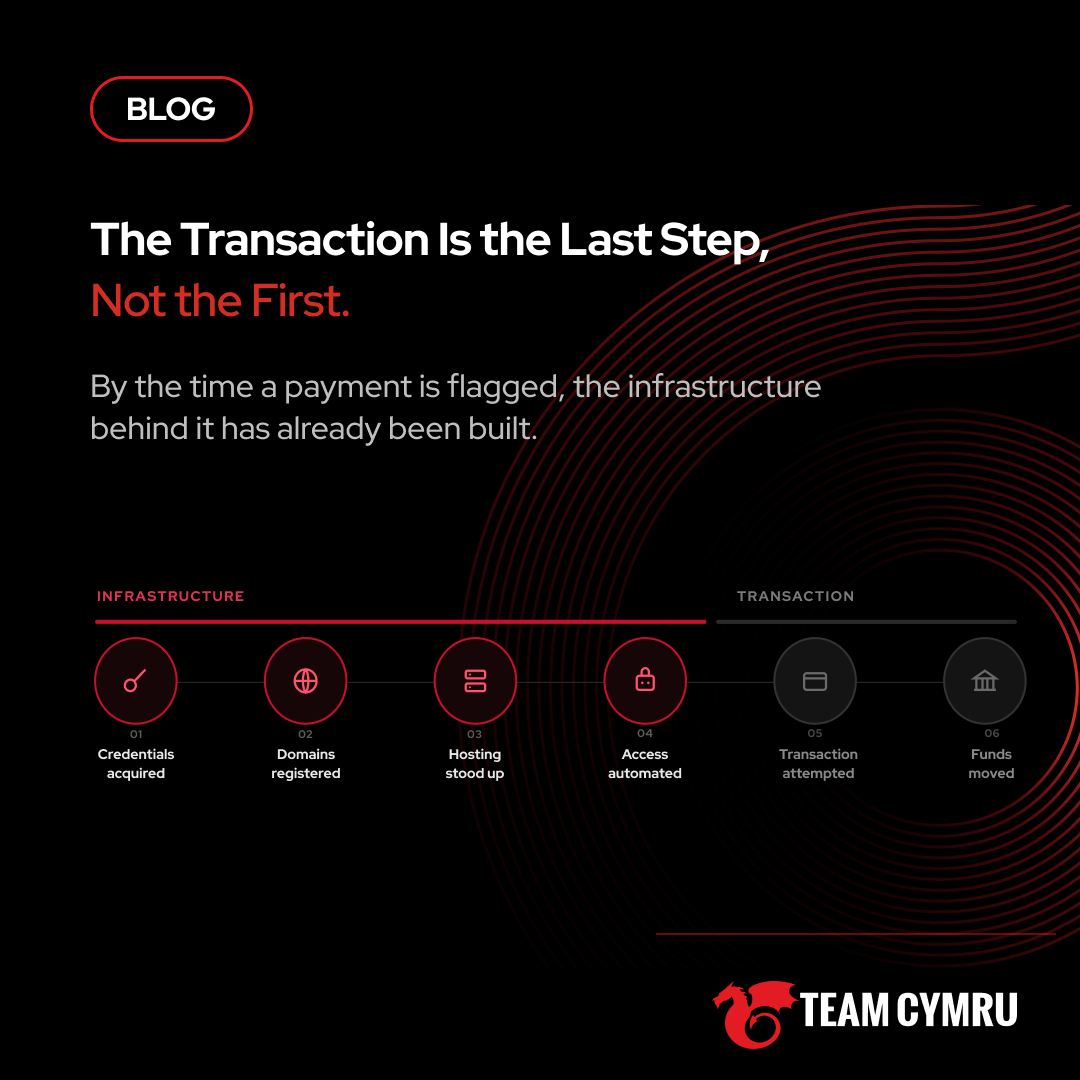
The transaction is the last step, not the first: spotting fraud attack patterns earlier with threat intelligence
3
min read

The Transaction Is the Last Step, Not the First

Cl0p Til You Drop: Cl0p ransomware threat intelligence research on managed file transfer attack campaigns
Eli Woodward
5
min read

Cl0p Til you Drop - 6 Years, 10 Campaigns, 8 Zero-Days

Products
Pure Signal™ CommandPure Signal™ ReconPure Signal™ ScoutPure Signal™ RadarMCP ServerTotal Insights Feed
Global Defender Exchange
Bogon NetworksDDOS Mitigation UTRSNimbus Threat MonitorMHR - APICSIRT Assistance ProgramIP-to-ASN Mapping
Support
0900-1700 ET
1400-2200 UTC
Submit a Ticketsupport@cymru.comPGP KeyEmergencies: +1 847-378-3301
Contact us
+1 847-378-3300
Follow Us
Team Cymru on LinkedInTeam Cymru on XTeam Cymru on YouTubeTeam Cymru on GitHub
© 2026 Team Cymru. All Rights Reserved.
GDPRPrivacy PolicyEU-U.S. Data Privacy PolicyModern Slavery Act