
From Serengeti to Serengeti III: What Three INTERPOL Operations Reveal
.png)
LegionRelay: Ukraine Targeted by Five Previously Unidentified C2 Servers

Relaying to the Frontier

From the Disk to the Flows: Ransomware Infrastructure Analysis

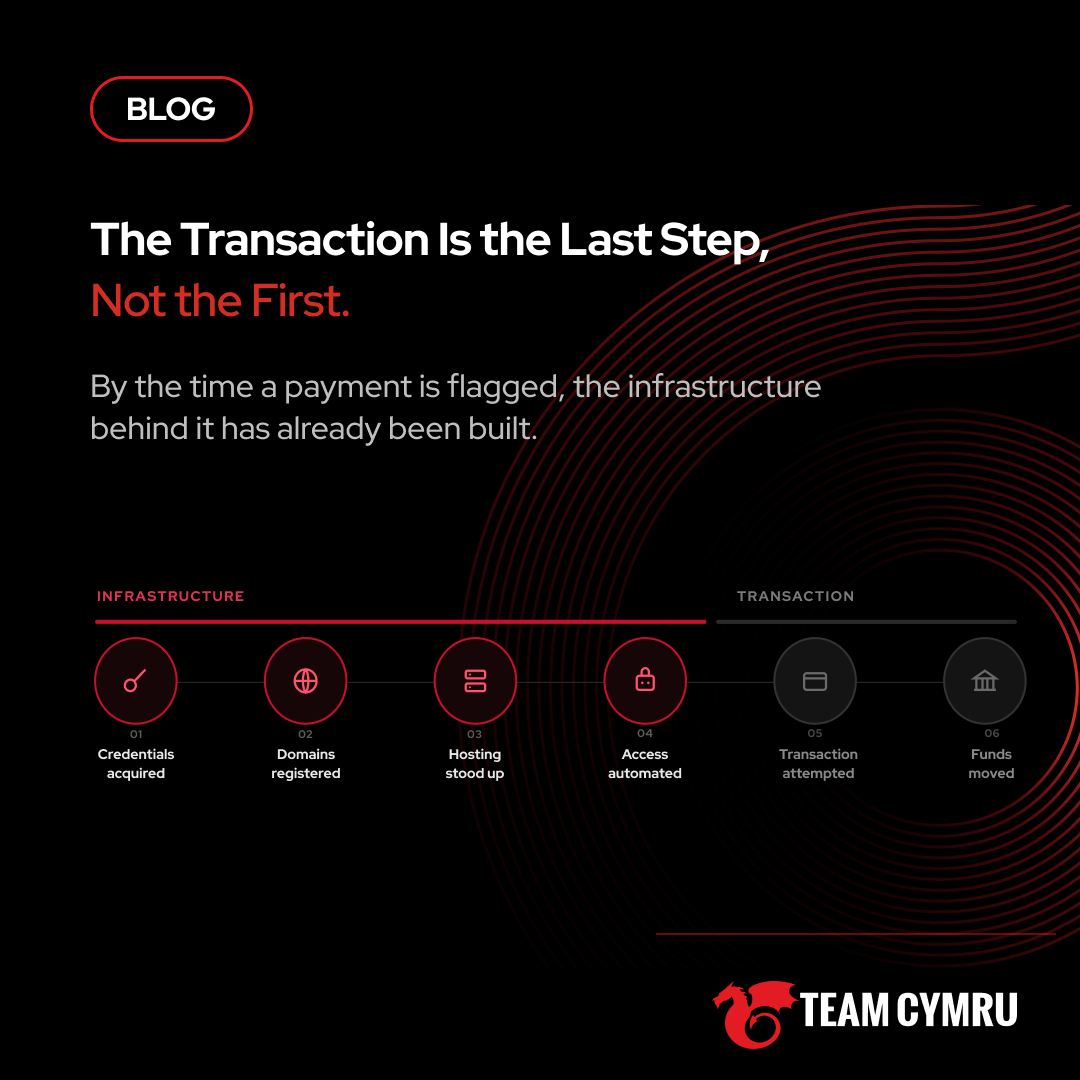
The Transaction Is the Last Step, Not the First

Behind the Panels: Validating ShinyHunters Cluster A Infrastructure Through Network Telemetry

From C2 Detection to Possible Victim Identification

Modernizing Incident Response: 4 Steps to Bulletproof Your Windows Logging

Cybercrime Doesn't Reinvent Itself. It Optimizes.
The Unclosed Gap: Why the 2026 DBIR Proves the Decisive Battle Happens Before the First Internal Alert

Targeting the Defense Industrial Base: What Network Telemetry Reveals About Nation-State Pre-Positioning
.png)
Unmasking DPRK Cyber Threat Actors: Fake IT Worker Infrastructure & Post-Exposure Analysis
.png)
Cyber Security Intelligence: Analysis of Edge Devices Amid Growing Vulnerabilities
.png)
Stranger Strings: Yurei Ransomware Operator Toolkit Exposed
.png)
Industrial Cybersecurity Risks from Internet-Exposed ICS Devices
.png)
From Developer to Product Owner: The Fundamental Shifts from Generative AI
.png)
Team Cymru Partners with DOJ to Disrupt World’s Largest IoT DDoS Botnets
.png)
The Beast Returns: Analysis of a Beast Ransomware Server
.png)
Duaine Labno on Digital Investigations and Corporate Threat Intelligence
.png)
Cybersecurity Incident Response at Thermo Fisher: How the Ransomware Landscape Has Evolved
.png)
GRIMBOLT C2 Infrastructure Recon: Pivoting From One IP to a Mapped Cluster
.png)
What Helping Secure SMBs Shows About Attack Trends
.png)
Tracking CyberStrikeAI Usage
.png)
What Cyber Insurance Claims Reveal About Real Cyber Risk

Team Cymru Partners with INTERPOL in Coordinated Operation Red Card 2.0
.png)
Fraud Intelligence at Stripe: Inside the Financial Fraud Kill Chain

Protecting Critical National Infrastructure (CNI) through extended global visibility
.png)
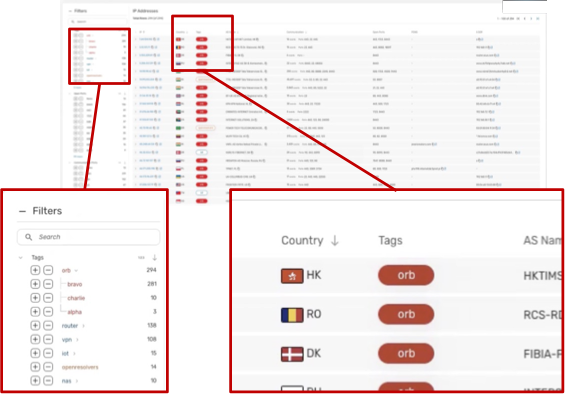
Tracking ORBs on Singapore's Telecommunications Networks
.png)
How AI-driven Threat Detection is Reshaping Threat Intelligence
.png)
MediaLand Isn't Dormant: The Reality of Active OFAC-Sanctioned Infrastructure
.png)
Payment Fraud Detection: How ATO and Phishing Kits Drive Modern Abuse
.png)
Operationalize Pure Signal™ in OpenCTI
.png)
From Raw Intelligence to Validation: Thoughts on Operationalizing MITRE from a Cyber Threat Intelligence Director
.png)
Scattered Spider Attacks | Infrastructure and TTP Analysis

Reducing Friction in Cyber Threat Intelligence: Views from a Director of Advanced Cyber Practices

Cybersecurity in the Public Sector: Two CISOs’ Views on the Future of Threat Intelligence

Team Cymru and OpenCTI: Better Together for Threat Intelligence

Analysing Carding Infrastructure
.png)
RADAR Offers Full External Asset Discovery at the Click of a Button

Team Cymru Supports INTERPOL in Coordinated Operation Across Africa as Part of Operation Sentinel

The Indictment Is the IOC: Using Legal Records to Hunt DPRK Remote Workers

Query Scout in Synapse Enterprise With New Power-Up for Team Cymru
.png)
From Discovery to Attribution, RADAR Makes Threat Hunting Seamless

RADAR Takes the Guess Work Out of Vulnerability Exposure Management

Team Cymru and Abusix Partner to Eradicate Botnets

Minimize Partner Risk with RADAR's Third-Party Infrastructure Mapping
.png)
With RADAR, Never Worry About Losing Sight of Exposed Assets

Team Cymru Supports Europol to Takedown of Three Key Cybercriminal Tools as Part of Operation Endgame

No Scans. No Noise. Just Complete Exposure Visibility

Team Cymru Supports INTERPOL’s Operation Serengeti 2.0 to Dismantle Cybercrime Networks Across Africa
Supercharge Threat Hunting: Team Cymru Pure Signal™ Scout Now Integrated with Google SecOps

Fingerprinting Malware C2s with Tags

Team Cymru Tags Explained: Powering Faster, Smarter Threat Intelligence

ToolShell, SharePoint, and the Death of the Patch Window

Supply Chain & CTI

Uncovering DPRK Remote Workers: Detecting Hidden Threats Through Internet Telemetry

Inside DanaBot’s Infrastructure: In Support of Operation Endgame II
.jpeg)
Understanding the Federal Compliance Landscape

Team Cymru Achieves ISO 27001 Re-Certification for Third Consecutive Year

New innovation helps Security Teams gain faster threat insights

Top 10 Predictions Shaping the Future of Cybersecurity in 2025 According to 35+ Experts
.png)
Splunk's Security Strategist on Building Effective Threat Hunting Programs

Google's Head of Security Architecture Shares Framework for Protecting AI Systems

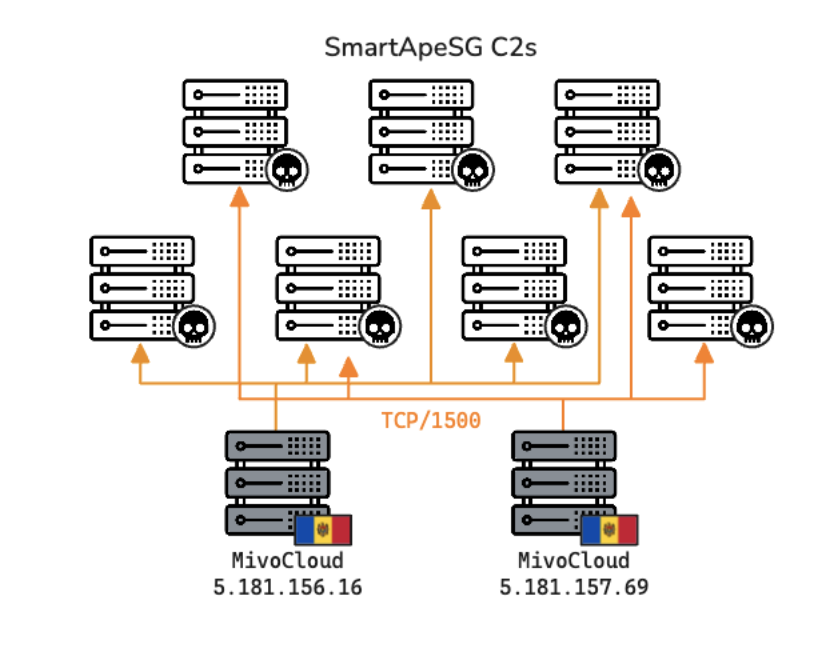
Tracing the Path From SmartApeSG to NetSupport RAT
.webp)
Building a More Resilient Security Strategy Through Threat Intelligence Integration

Eating Your Own Dog Food

DORA Regulation (Digital Operational Resilience Act): A Threat Intelligence Perspective

A Primer on JA4+: Empowering Threat Analysts with Better Traffic Analysis

Jingle Shells: How Virtual Offices Enable a Facade of Legitimacy

2024 Year in Review: Features and Improvements in Pure Signal™ Scout

Team Cymru Honored with Third Consecutive Gold HIRE Vets Medallion Award from U.S. Department of Labor

Celebrating a Milestone - Over 1.5 Billion Daily Queries on Our IP to ASN Mapping Service

Team Cymru Supports INTERPOL’s Operation Synergia II to Dismantle 22,000 Cybercrime Servers

An Introduction to Operational Relay Box (ORB) Networks - Unpatched, Forgotten, and Obscured

Announcing the Team Cymru Scout Integration With Palo Alto Cortex XSOAR

Talent and Technology: Bridging the Gap in Modern Threat Hunting Programs

What is Threat Intelligence?

How Effective Threat Hunting Programs are Shaping Cybersecurity

The Evolution of Threat Hunting

Insights into a “Cyber Attack” against the Venezuelan National Electoral Council

How Security Teams are Strengthening Their Threat Hunting

FIN7: The Truth Doesn't Need to be so STARK

Botnet 7777: Are You Betting on a Compromised Router?

Navigating the Evolving Landscape of Cybersecurity

How the New Splunk App for Scout Can Enrich and Accelerate Your Investigations
The Importance of Real-Time Insights for SOC Security Analysts
Want to learn more about NetFlow? Here's a useful analogy to get you started
Latrodectus: This Spider Bytes Like Ice
Insights into Internet Outages along Africa's Western Coast
Peer Reviews - Why Peer Reviews Matter

Threat Intelligence: A CISO ROI Guide - Elite Threat Hunters Prevent Supply Chain Breaches

Senior Stakeholder explainer for Octo Malware

Coper / Octo - A Conductor for Mobile Mayhem… With Eight Limbs?

Navigating Cybersecurity Frontiers in Rwanda: Unveiling the RISE Conference's Agenda

Continuous Threats Need Continuous Management
Risk Modeling and Real-Time Intelligence - Part 2

Risk Modeling and Real-Time Intelligence - Part 1
Threat Modeling and Real-Time Intelligence - Part 2

.png)